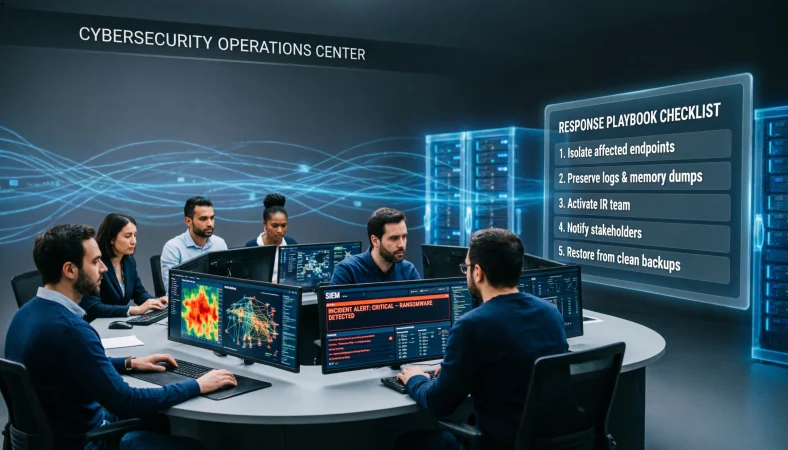
Quick Answer: A cyber security incident response playbook gives teams a clear, repeatable way to respond when something goes wrong, from suspicious logins and malware alerts to data breaches and system outages. It helps people know what to do, who to notify, and how to move from panic to action.
Top alternatives: cybersecurity incident response plan, security incident response checklist, incident response procedure, cyber incident response guide, security breach response plan
A good cyber security incident response playbook is basically the workplace version of having a fire escape plan. Nobody wants to use it, but everyone is happier when they know where to go when alarms start going off. Whether the situation involves a phishing email, compromised account, ransomware alert, suspicious network activity, or an unexpected security notification, having a structured response makes communication much easier. The right wording also matters when teams are texting, emailing, posting updates, or coordinating during a stressful incident.
You do not want five people saying five different things while the clock is ticking. A strong playbook helps turn confusion into coordinated action, giving everyone a clearer idea of what happens next. It can also make training, tabletop exercises, internal communication, and post-incident reviews much smoother. In short, preparation may not feel exciting, but it beats improvising when the security dashboard starts looking like it has personal beef with everyone.
Funny Cyber Security Incident Response Playbook Responses
“Well, that escalated from zero to incident.”
Use this for a light internal comment when a routine alert suddenly becomes a confirmed security issue.
Meaning: The situation became serious much faster than expected.
“The firewall has entered its main-character era.”
Use this when security controls are suddenly generating a flood of alerts.
Meaning: The security system is demanding everyone’s attention.
“Nobody panic. The playbook has entered the chat.”
Use this to lighten the mood while reminding the team to follow established procedures.
Meaning: The response process is ready to guide the team.
“Today’s agenda: coffee, alerts, controlled chaos.”
Use this for an internal training session or tabletop exercise with a playful tone.
Meaning: Incident response can become hectic, but the team is prepared.
“Plot twist: it was not just a weird login.”
Use this when an investigation reveals that an apparently minor alert needs deeper attention.
Meaning: The initial assumption changed as evidence emerged.
“Security incident? On a Monday? Bold choice.”
Use this for a lighthearted internal message during an inconvenient incident.
Meaning: The timing could hardly be less convenient.
“The logs have receipts.”
Use this when investigation data is helping establish what happened.
Meaning: Available evidence may reveal important details about the incident.
“Everyone stay calm and open the checklist.”
Use this when reminding colleagues not to improvise during an incident.
Meaning: The team should rely on established procedures.
“Our incident response plan just got promoted to VIP.”
Use this when a security event makes the playbook especially important.
Meaning: The response plan has become central to the situation.
“The alert said hello, and nobody liked the greeting.”
Use this when a security notification turns out to be concerning.
Meaning: The alert created immediate concern.
“Time to turn panic into paperwork.”
Use this when moving from initial reaction into structured documentation.
Meaning: The team should document actions instead of reacting randomly.
“Cybersecurity: where ‘interesting’ is rarely a compliment.”
Use this as a humorous training or awareness line.
Meaning: Unexpected security events usually deserve careful investigation.
Professional Cyber Security Incident Response Playbook Responses
“Please follow the documented incident response procedure.”
Use this when directing team members toward the approved response process.
Meaning: Established procedures should guide the next steps.
“Let’s confirm the incident scope before taking further action.”
Use this when the available information is incomplete.
Meaning: Decisions should be based on verified facts and known impact.
“Please document all actions taken during the response.”
Use this when maintaining an incident timeline is important.
Meaning: Accurate records should be preserved throughout the investigation.
“Let’s identify the appropriate incident owner and escalation path.”
Use this when responsibilities need to be clarified.
Meaning: The right people should be assigned to coordinate the response.
“We should preserve relevant evidence before making changes.”
Use this when investigation data may be important for understanding the incident.
Meaning: Potentially useful evidence should not be unnecessarily altered.
“Please escalate this according to the severity criteria.”
Use this when an event may require additional expertise or authority.
Meaning: The incident should move through the organization’s defined escalation process.
“Let’s establish what we know, what we do not know, and what we need to verify.”
Use this during an incident briefing when information is still developing.
Meaning: Separating facts from assumptions improves decision-making.
“We need a clear timeline of events before closing the incident.”
Use this during investigation or post-incident review.
Meaning: Understanding the sequence of events helps establish what occurred.
“Let’s keep communications factual, concise, and consistent.”
Use this when multiple teams are communicating about the same incident.
Meaning: Consistent messaging reduces confusion.
“Please confirm containment status before proceeding.”
Use this when the team needs to know whether the immediate threat is controlled.
Meaning: The response should account for the current containment state.
“Let’s coordinate technical and business stakeholders.”
Use this when an incident affects more than the security team.
Meaning: Relevant teams should work from the same understanding of the situation.
“We can move to recovery once the appropriate criteria are met.”
Use this when discussing the transition from containment into recovery.
Meaning: Recovery should follow defined conditions rather than guesswork.
Clever Cyber Security Incident Response Playbook Responses
“Detect first, guess later.”
Use this as a memorable reminder during security training.
Meaning: Evidence should come before assumptions.
“The fastest response starts with knowing the next step.”
Use this when explaining why playbooks matter.
Meaning: Preparation reduces hesitation during incidents.
“A good playbook turns ‘What now?’ into ‘Step one.’”
Use this in awareness material or internal training.
Meaning: Structured procedures make uncertain situations easier to manage.
“Alerts tell you something happened; investigation tells you what.”
Use this when teaching the difference between detection and analysis.
Meaning: An alert is only the beginning of understanding an incident.
“Contain the problem before it becomes tomorrow’s problem.”
Use this when emphasizing timely containment.
Meaning: Early action can limit the potential spread or impact of an incident.
“Document today so nobody has to reconstruct yesterday.”
Use this when encouraging detailed incident records.
Meaning: Timely documentation makes later analysis easier.
“A playbook is preparation wearing a checklist.”
Use this as a memorable training phrase.
Meaning: A playbook turns preparedness into practical steps.
“Good incident response is teamwork with timestamps.”
Use this when explaining why coordination and documentation matter.
Meaning: Collaboration and accurate timing are both important during response.
“Do not let one alert become five assumptions.”
Use this when encouraging evidence-based investigation.
Meaning: A single alert should not automatically lead to unsupported conclusions.
“When the situation changes, the response should change with it.”
Use this when explaining why playbooks need decision points.
Meaning: Response actions should adapt to new information.
“Clarity is a security control too.”
Use this when discussing communication during incidents.
Meaning: Clear information can help teams coordinate effectively.
“The best emergency message answers ‘what happened’ and ‘what next.’”
Use this when creating internal incident updates.
Meaning: Useful communications should explain both the situation and the next action.
Polite Cyber Security Incident Response Playbook Responses
“Could everyone please follow the documented response steps?”
Use this when gently redirecting a team toward the approved procedure.
Meaning: The team should use the established process.
“Please share any verified information with the response team.”
Use this when gathering useful details without encouraging speculation.
Meaning: Confirmed information can support the investigation.
“Could we pause changes until the response team confirms the next step?”
Use this when unnecessary system changes could interfere with investigation.
Meaning: Coordinated action is preferable to independent changes.
“Please keep the incident channel focused on relevant updates.”
Use this when communication is becoming cluttered.
Meaning: Important information should remain easy to find.
“Could you confirm whether the alert has been investigated?”
Use this when checking status professionally.
Meaning: The response team needs confirmation of the investigation state.
“Please let us know if you notice anything unusual.”
Use this when gathering observations from employees or stakeholders.
Meaning: Additional observations may help identify the incident’s scope.
“Let’s make sure everyone has the same information.”
Use this when different teams appear to have different understandings.
Meaning: Shared information supports coordinated response.
“Could we document that decision for the incident record?”
Use this when an important response decision has been made.
Meaning: Significant decisions should be preserved for later review.
“Please avoid forwarding unverified information.”
Use this when preventing rumors during an active incident.
Meaning: Communications should remain accurate.
“Let’s confirm the appropriate escalation contact.”
Use this when responsibility or escalation ownership is unclear.
Meaning: The team should identify the correct person to involve.
“Thank you for flagging this promptly.”
Use this when acknowledging someone who reported a suspicious event.
Meaning: Timely reporting is appreciated and useful.
“We’ll share an update once the information has been verified.”
Use this when stakeholders are asking for details that are still being investigated.
Meaning: Updates should be based on confirmed information.
Creative Cyber Security Incident Response Playbook Responses
“From first alert to final recovery, give every step a job.”
Use this when designing or reviewing an incident workflow.
Meaning: Every stage should have a clear purpose.
“Build the playbook like a map, not a maze.”
Use this when making response documentation easier to navigate.
Meaning: Procedures should be clear and practical.
“Every incident deserves a beginning, middle, and documented ending.”
Use this when teaching incident lifecycle concepts.
Meaning: Response should cover detection through closure and review.
“Turn security chaos into a sequence of small decisions.”
Use this when explaining how playbooks simplify stressful events.
Meaning: Breaking response into manageable steps improves clarity.
“Give every alert a destination.”
Use this when creating triage procedures.
Meaning: Alerts should have defined ownership or handling paths.
“Write the playbook for your busiest day, not your quietest one.”
Use this when reviewing response documentation.
Meaning: Procedures should remain useful under pressure.
“Make the next action obvious.”
Use this when improving the readability of a response procedure.
Meaning: Users should quickly understand what to do next.
“Build for humans, because humans will run the incident.”
Use this when designing practical security procedures.
Meaning: Playbooks should be understandable and usable by real teams.
“Every escalation path should have a name behind it.”
Use this when documenting incident responsibilities.
Meaning: Teams need identifiable owners for escalation points.
“If the playbook needs a treasure map, simplify it.”
Use this humorously when reviewing overly complicated documentation.
Meaning: Response instructions should be easy to navigate.
“Make important information impossible to miss.”
Use this when improving incident documentation.
Meaning: Critical actions and contacts should be highly visible.
“A memorable playbook gets used when memory gets busy.”
Use this when discussing usability and training.
Meaning: Clear procedures help when people are under pressure.
Sarcastic Cyber Security Incident Response Playbook Responses
“Because apparently ‘hope for the best’ was not an approved control.”
Use this during security training when emphasizing formal response procedures.
Meaning: Wishful thinking is not a substitute for preparation.
“Nothing says productivity like an unexpected security incident.”
Use this as light workplace humor during a stressful response.
Meaning: Security incidents can disrupt normal work.
“Excellent, another alert for the collection.”
Use this when a team receives yet another notification during a busy period.
Meaning: The team is dealing with a growing number of alerts.
“Sure, let’s improvise during the incident. What could possibly happen?”
Use this to jokingly discourage people from ignoring the playbook.
Meaning: Improvisation can create unnecessary risk.
“The spreadsheet of doom has officially been updated.”
Use this when documenting a growing incident timeline or action list.
Meaning: The incident record is becoming increasingly important.
“Nothing suspicious here, except everything.”
Use this when several indicators require investigation.
Meaning: Multiple signs are creating concern.
“The logs are having another character-building moment.”
Use this when an investigation involves messy or complicated logs.
Meaning: Reviewing evidence is becoming challenging.
“Fantastic timing, security incident.”
Use this when an incident arrives during an inconvenient moment.
Meaning: The timing is frustrating.
“Because one incident response meeting was apparently not enough.”
Use this when a situation requires repeated coordination.
Meaning: The incident is demanding more attention than expected.
“Let’s all pretend the alert never happened. Just kidding.”
Use this as a playful reminder not to ignore security warnings.
Meaning: Security alerts need proper attention.
“The playbook called. It would like everyone to stop freelancing.”
Use this when team members are taking inconsistent actions.
Meaning: Everyone should follow the coordinated response process.
“Another day, another reason to document everything.”
Use this when emphasizing incident records.
Meaning: Good documentation remains valuable during security events.
Calm And Casual Cyber Security Incident Response Playbook Responses
“No panic, just follow the steps.”
Use this when keeping a team focused during an incident.
Meaning: Calm execution is more useful than panic.
“Let’s take this one step at a time.”
Use this when the incident feels overwhelming.
Meaning: Breaking the response into stages can make it manageable.
“We’ve got a process for this.”
Use this when reassuring colleagues that an established procedure exists.
Meaning: The team has a structured response available.
“Let’s stick to the facts for now.”
Use this when speculation starts spreading.
Meaning: Verified information should guide the response.
“First things first, let’s confirm what happened.”
Use this when the initial alert is unclear.
Meaning: The team should establish basic facts before making decisions.
“One alert at a time.”
Use this when multiple notifications arrive simultaneously.
Meaning: The team should prioritize and work through issues systematically.
“Let’s keep the channel clear and useful.”
Use this when incident communications become crowded.
Meaning: Important updates should remain easy to find.
“We’ll figure out the next step from the evidence.”
Use this when the situation is still developing.
Meaning: Response decisions should be informed by investigation.
“No guessing needed, the procedure is right there.”
Use this when reminding someone to consult the playbook.
Meaning: The established process should guide the response.
“Let’s get everyone on the same page.”
Use this when coordinating multiple responders.
Meaning: Shared understanding helps the response run smoothly.
“We can handle this one step at a time.”
Use this when reassuring a stressed team.
Meaning: The incident can be approached through manageable actions.
“Keep calm, keep notes, keep moving.”
Use this as a memorable reminder during response activities.
Meaning: Calm action and documentation should continue throughout the incident.
Confident Cyber Security Incident Response Playbook Responses
“We know the process, so let’s work the process.”
Use this when a team needs confidence during an active incident.
Meaning: Established procedures provide a practical path forward.
“Let’s move with purpose and verify as we go.”
Use this when encouraging timely but careful response.
Meaning: Speed should be balanced with evidence.
“The next step is clear.”
Use this when the playbook identifies the appropriate action.
Meaning: The team has enough information to proceed.
“We’ll establish the facts and respond accordingly.”
Use this during an incident briefing.
Meaning: Evidence will guide the response.
“Everyone knows their role. Let’s execute.”
Use this when responsibilities have already been assigned.
Meaning: The team should carry out its defined responsibilities.
“We are documenting the timeline as we respond.”
Use this when reassuring stakeholders that the event is being tracked.
Meaning: Response actions and timing are being recorded.
“We’ll escalate when the criteria are met.”
Use this when discussing escalation decisions.
Meaning: Escalation will follow established thresholds.
“Containment comes first when the situation requires it.”
Use this when discussing immediate response priorities.
Meaning: Limiting ongoing impact can be a key response objective.
“Let’s make decisions based on evidence.”
Use this when correcting assumptions during an investigation.
Meaning: Verified information should drive action.
“We have a documented route from detection to recovery.”
Use this when explaining the value of a complete playbook.
Meaning: The response process covers multiple stages.
“Clear roles make fast response possible.”
Use this when explaining why responsibilities should be documented.
Meaning: Knowing who does what can reduce delays.
“Prepared teams respond with less hesitation.”
Use this during cybersecurity awareness training.
Meaning: Preparation can make response actions more organized.
Emotional Cyber Security Incident Response Playbook Responses
“Nobody wants an incident, but preparation gives the team something solid to lean on.”
Use this when acknowledging the stress surrounding cybersecurity events.
Meaning: Preparation can provide structure during uncertainty.
“It is okay to feel overwhelmed, but the next step still matters.”
Use this when supporting people during a stressful response.
Meaning: A difficult situation can still be approached through manageable actions.
“Good preparation helps people stay focused when pressure rises.”
Use this during security awareness discussions.
Meaning: Planning can support calm decision-making.
“Behind every alert is a team trying to protect something important.”
Use this when making security training feel more human.
Meaning: Security response ultimately supports people, systems, and business operations.
“The goal is not perfection; it is a clear and coordinated response.”
Use this when reassuring teams during exercises or incidents.
Meaning: Effective coordination matters more than pretending mistakes are impossible.
“When things get stressful, structure matters even more.”
Use this when explaining why playbooks should be accessible.
Meaning: Clear procedures become particularly useful under pressure.
“Every documented lesson makes the next response stronger.”
Use this during post-incident reviews.
Meaning: Lessons learned can improve future preparedness.
“A good response protects more than systems; it protects trust.”
Use this when discussing the broader impact of security incidents.
Meaning: How an organization responds can affect confidence and relationships.
“Preparation is one less thing to worry about when the unexpected happens.”
Use this when encouraging teams to practice incident response.
Meaning: Preparation can reduce uncertainty.
“The people responding deserve clear instructions too.”
Use this when advocating for usable playbooks.
Meaning: Response documentation should support the people expected to use it.
“A calm response can start with a well-prepared plan.”
Use this when explaining the relationship between preparation and composure.
Meaning: Planning can create a clearer path through stressful events.
“Every incident can teach the team something worth remembering.”
Use this during lessons-learned discussions.
Meaning: Post-incident learning can improve future response.
Sweet Cyber Security Incident Response Playbook Responses
“Thanks for helping keep everyone informed.”
Use this when acknowledging someone who provides useful incident updates.
Meaning: Their communication is appreciated.
“Good catch. Reporting it early really matters.”
Use this when thanking someone for flagging a suspicious event.
Meaning: Early reporting can help the response team investigate promptly.
“Appreciate everyone sticking to the process.”
Use this after a coordinated response or exercise.
Meaning: Following procedures contributed to organized teamwork.
“Thanks for keeping the incident record updated.”
Use this when recognizing careful documentation.
Meaning: Accurate records are valuable during response.
“Teamwork makes incident response a lot smoother.”
Use this during training or after an exercise.
Meaning: Collaboration supports effective coordination.
“Thank you for asking before making a change.”
Use this when someone appropriately checks with the response team.
Meaning: Coordinated action can help avoid unnecessary complications.
“Every careful update helps the bigger picture.”
Use this when acknowledging useful information from different team members.
Meaning: Small verified details can contribute to understanding an incident.
“You did the right thing by reporting it.”
Use this when encouraging employees to report suspicious activity.
Meaning: Reporting concerns is an important part of security awareness.
“Thanks for keeping communication clear.”
Use this after a well-managed incident communication.
Meaning: Clear communication helps teams stay coordinated.
“Appreciate everyone keeping calm and focused.”
Use this when thanking responders after a stressful event.
Meaning: Composure supported an organized response.
“Good preparation really shows when things get complicated.”
Use this after a tabletop exercise or real incident.
Meaning: Preparation becomes valuable when circumstances become difficult.
“Thanks for being part of the response team effort.”
Use this when recognizing collective participation.
Meaning: Every appropriate contribution can support the overall response.
Dramatic Cyber Security Incident Response Playbook Responses
“The alert arrives. The room goes silent. The playbook opens.”
Use this as dramatic copy for cybersecurity awareness content.
Meaning: The team is moving from surprise into structured response.
“One suspicious login. One very important investigation.”
Use this when creating attention-grabbing training material.
Meaning: A seemingly small event may deserve investigation.
“The clock is ticking, and the response plan is ready.”
Use this when emphasizing the importance of preparation.
Meaning: Prepared procedures can support timely action.
“Tonight, the logs tell the story.”
Use this as dramatic wording for an incident exercise.
Meaning: Investigation evidence may help reconstruct events.
“The incident has entered stage two.”
Use this during a tabletop scenario involving escalating events.
Meaning: The situation has progressed to another response phase.
“Every minute adds another piece to the puzzle.”
Use this when describing an ongoing investigation.
Meaning: New information can gradually clarify what happened.
“The system raised the alarm. Now the team answers.”
Use this for security awareness content.
Meaning: Detection needs an organized human response.
“The playbook is open. The roles are assigned. Let’s begin.”
Use this to introduce an incident response exercise.
Meaning: The team is prepared to start the coordinated response.
“The first clue has arrived.”
Use this when beginning a fictional or tabletop security scenario.
Meaning: The investigation has received its initial useful indicator.
“Containment is not the finale. It is the turning point.”
Use this when teaching that response continues beyond initial containment.
Meaning: Containment is one stage within a broader response lifecycle.
“The incident may be unexpected. The response should not be.”
Use this as a memorable cybersecurity training statement.
Meaning: Preparation should make the response more predictable.
“When the alert becomes real, preparation becomes action.”
Use this when motivating teams to practice response procedures.
Meaning: Exercises help translate planning into practical behavior.
Thoughtful Cyber Security Incident Response Playbook Responses
“A playbook should answer the questions people are most likely to ask under pressure.”
Use this when reviewing the usefulness of response documentation.
Meaning: Good procedures anticipate real-world uncertainty.
“The best response process balances urgency with careful judgment.”
Use this when discussing incident decision-making.
Meaning: Teams need to act promptly without abandoning verification.
“Every response should leave the organization with better knowledge than it started with.”
Use this during post-incident planning.
Meaning: Lessons learned should improve future preparedness.
“Clarity becomes especially valuable when information is incomplete.”
Use this when explaining incident communication.
Meaning: Clear distinctions between facts and unknowns help teams respond responsibly.
“A playbook should be practical enough to use during a stressful Tuesday afternoon.”
Use this when testing whether procedures are genuinely usable.
Meaning: Documentation should work in ordinary real-world pressure, not just theory.
“Good preparation includes knowing when to ask for help.”
Use this when defining escalation procedures.
Meaning: Teams should recognize when additional expertise is needed.
“The response process should make responsibilities obvious.”
Use this when reviewing ownership and escalation paths.
Meaning: People should know what they are responsible for.
“Incident documentation is not just paperwork; it is organizational memory.”
Use this during post-incident review discussions.
Meaning: Records preserve useful knowledge for future teams.
“The response should protect both immediate operations and long-term lessons.”
Use this when discussing the full incident lifecycle.
Meaning: Recovery and learning are both important outcomes.
“Practice reveals gaps that documentation alone can hide.”
Use this during tabletop exercise planning.
Meaning: Exercises can reveal practical weaknesses in a response process.
“A useful playbook tells people what to do without making them decode it first.”
Use this when improving response documentation.
Meaning: Instructions should be direct and easy to understand.
“The strongest response habits are built before the incident begins.”
Use this when encouraging regular training and exercises.
Meaning: Preparation is most useful when established in advance.
Direct Cyber Security Incident Response Playbook Responses
“Open the playbook and start with the documented first step.”
Use this when an incident has been identified and responders need direction.
Meaning: The response should begin with the established procedure.
“Confirm the alert before escalating the situation.”
Use this when the initial notification requires validation.
Meaning: Verification should inform the next action.
“Assign an incident owner.”
Use this when responsibility is unclear.
Meaning: A designated owner should coordinate the response.
“Record the time, action, and decision.”
Use this when maintaining an incident timeline.
Meaning: Key response details should be documented.
“Escalate according to the defined severity.”
Use this when an event meets established escalation criteria.
Meaning: Escalation should follow documented thresholds.
“Preserve relevant evidence.”
Use this when investigation data may be important.
Meaning: Potential evidence should be protected from unnecessary alteration.
“Keep stakeholders updated with verified information.”
Use this during ongoing incident communication.
Meaning: Stakeholders should receive accurate updates.
“Do not improvise when the procedure already covers the situation.”
Use this when redirecting responders toward the established process.
Meaning: Existing guidance should be used where applicable.
“Confirm containment before moving forward.”
Use this when determining whether the immediate issue has been controlled.
Meaning: The team should verify containment status.
“Document unresolved questions before closing the incident.”
Use this during final review.
Meaning: Open issues should be recorded rather than forgotten.
“Complete the recovery steps in the approved sequence.”
Use this during the recovery stage.
Meaning: Recovery should follow the organization’s defined process.
“Schedule the post-incident review.”
Use this after immediate response activities are complete.
Meaning: The organization should review what happened and identify lessons.
Practical Cyber Security Incident Response Playbook Responses
“Start with detection, then move through triage, containment, investigation, recovery, and review.”
Use this when explaining the broad flow of incident response.
Meaning: A structured lifecycle helps organize response activities.
“Give every incident a severity level and an owner.”
Use this when building an incident management workflow.
Meaning: Clear classification and ownership support coordination.
“Keep the contact list current.”
Use this when maintaining the operational side of a playbook.
Meaning: Outdated contacts can create avoidable delays.
“Write escalation criteria in plain language.”
Use this when improving playbook usability.
Meaning: Responders should understand when escalation is required.
“Include decision points, not just instructions.”
Use this when creating a flexible response process.
Meaning: Incident conditions can vary, so responders need guidance for different scenarios.
“Add templates for incident updates.”
Use this when preparing communication sections.
Meaning: Prewritten structures can make urgent communication easier.
“Test the playbook before you need it.”
Use this when encouraging tabletop exercises.
Meaning: Practice can reveal weaknesses before a real incident occurs.
“Review the playbook after significant incidents.”
Use this when establishing continuous improvement.
Meaning: Real events can reveal where procedures need updating.
“Keep technical and business actions connected.”
Use this when designing cross-functional response procedures.
Meaning: Security actions can affect wider business operations.
“Make critical information easy to find.”
Use this when improving response documentation.
Meaning: Responders should not waste time searching for essential details.
“Define who can make key response decisions.”
Use this when documenting authority during incidents.
Meaning: Decision ownership should be clear before an incident occurs.
“Keep the playbook current as systems and threats change.”
Use this during regular security documentation reviews.
Meaning: Response procedures need ongoing maintenance.
FAQs
What is a cyber security incident response playbook? A cyber security incident response playbook is a structured set of instructions that helps an organization respond consistently to specific types of security incidents.
What does a cyber security incident response playbook usually include? It may include incident identification, severity classification, roles, escalation procedures, containment actions, communications, recovery guidance, documentation requirements, and post-incident review steps.
Is a cyber security incident response playbook the same as an incident response plan? Not always. A plan often describes the broader response strategy, roles, and governance, while a playbook can provide more specific procedures for particular incident scenarios.
Can a cyber security incident response playbook be used for phishing incidents? Yes. Organizations commonly create scenario-specific procedures for events such as phishing, compromised accounts, malware, suspicious access, ransomware, and data security incidents.
Should a cyber security incident response playbook be used during a tabletop exercise? Yes. A tabletop exercise can help teams practice the procedures, communication paths, escalation decisions, and responsibilities described in the playbook.
What if the incident does not match the playbook exactly? Use the closest applicable procedure, document important decisions, escalate when appropriate, and adapt based on verified information and organizational policy.
Should employees outside the security team know about the playbook? They should generally know the relevant reporting and escalation steps that apply to their role, even if they do not need access to every technical procedure.
Can a cyber security incident response playbook improve communication? Yes. Clearly defined roles, escalation paths, update templates, and communication responsibilities can make incident messaging more consistent.
What should you say if you do not know whether something is a security incident? A simple response is, “I noticed something unusual and wanted to report it so the appropriate team can review it.” Reporting uncertainty is usually better than silently ignoring a potentially important signal.
Can humor be used in cybersecurity incident response training? Yes, when appropriate. Light humor can make training memorable, but active incidents and sensitive communications should remain professional and factual.
How often should a cyber security incident response playbook be reviewed? It should be reviewed regularly and whenever major systems, responsibilities, technologies, business processes, or lessons from incidents change.
Why are clear response roles important? Clear roles reduce confusion by helping people understand who investigates, who communicates, who approves key decisions, and who coordinates escalation.
Conclusion
A cyber security incident response playbook does more than sit quietly in a document folder waiting for its big moment. It gives teams a practical path when alerts, suspicious activity, or security incidents create pressure. The right response language can also make communication clearer, calmer, and more consistent across security teams, managers, employees, and stakeholders.
Whether you need something professional, direct, thoughtful, clever, or a little funny for training, the goal is the same: make the next action easier to understand. Try different response styles, adapt them to your organization’s environment, and keep the ones that genuinely help. Save this list, share it with your team, and keep building a response process people can actually use.