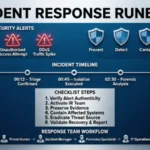
Quick Answer: Cyber incident response management is the organized process of detecting, containing, investigating, and recovering from cybersecurity incidents while keeping communication clear. These ready-to-use responses help teams communicate quickly during security events.
Top alternatives: Security Incident Management, Cybersecurity Incident Response, Incident Response Planning, Security Breach Response, Cyber Incident Management
A cyber incident can turn a normal workday into a full-on digital fire drill. One minute, everyone is answering emails, checking dashboards, or sending DMs. The next, someone spots suspicious activity, an account gets locked, or an alert starts lighting up the screen. That is where cyber incident response management becomes important.
Good incident response is not only about technical actions. It is also about knowing what to communicate, when to communicate it, and how to keep messages clear when pressure is high. Security teams need concise updates for coworkers, managers, customers, vendors, and leadership. A vague message can create confusion, while a calm and specific response can keep everyone moving in the same direction.
Whether you are creating an incident response plan, updating a team during an investigation, or documenting a security event, the right wording matters. The examples below provide practical, professional, conversational, and situation-specific responses you can adapt without making every message sound like it came from a corporate robot.
Funny Responses
1. The firewall is having a main-character moment.
Use this when a security alert appears and your team uses light humor internally.
Meaning: The incident is getting unusual attention while the team stays calm.
2. Our inbox just received a cybersecurity plot twist.
Use this when an unexpected security notification interrupts a normal workday.
Meaning: Something unexpected has happened and needs investigation.
3. The alerts have entered the group chat.
Use this when multiple security notifications suddenly start appearing.
Meaning: The incident has become noticeable across the team.
4. Today’s surprise feature is definitely not a feature.
Use this when suspicious system behavior appears unexpectedly.
Meaning: The unexpected behavior should be treated as a potential security issue.
5. Someone tell the incident response team that the party has started.
Use this internally when a confirmed alert triggers response procedures.
Meaning: The team needs to activate its incident response process.
6. Our security dashboard chose violence today.
Use this for lighthearted internal commentary during a stressful alert period.
Meaning: The security environment is unusually busy.
7. The server just sent us an interesting little mystery.
Use this when an investigation has started around unexplained activity.
Meaning: The team needs to determine what caused the unusual behavior.
8. Cybersecurity called, and apparently it wants attention.
Use this when a significant alert needs immediate team awareness.
Meaning: The security event deserves prompt attention.
9. Nothing says Monday like an unexpected security alert.
Use this when an incident begins during an otherwise ordinary workday.
Meaning: A routine day has suddenly become a security response situation.
Professional Responses
1. We have identified a potential cybersecurity incident and are investigating it.
Use this for an initial internal notification when suspicious activity requires review.
Meaning: The team has detected something concerning but is still establishing the facts.
2. The incident response process has been activated.
Use this after the event reaches the threshold for formal response.
Meaning: Established procedures are now guiding the investigation.
3. Our security team is assessing the scope and potential impact.
Use this in an early status update before the investigation is complete.
Meaning: The team is determining how extensive the incident may be.
4. Containment measures are currently being evaluated and implemented.
Use this when responders are working to limit further impact.
Meaning: The team is taking steps to control the incident.
5. We are continuing to monitor the environment for additional indicators.
Use this during active investigation and monitoring.
Meaning: Analysts are watching systems for related suspicious activity.
6. The available evidence is being reviewed to establish the incident timeline.
Use this when investigators are reconstructing what happened.
Meaning: The team is using evidence to understand the sequence of events.
7. Relevant stakeholders have been notified according to our response procedures.
Use this when required internal parties have received an update.
Meaning: Communication is following the organization’s incident process.
8. We are prioritizing service continuity while addressing the security issue.
Use this when business operations must continue during response activities.
Meaning: The team is balancing security actions with operational needs.
9. The incident remains under active investigation.
Use this when there is not enough verified information for a final conclusion.
Meaning: The investigation is ongoing and details may change.
Technical Responses
1. We are validating the alert against available telemetry and log data.
Use this when security analysts are determining whether an alert represents real malicious activity.
Meaning: The alert is being checked against technical evidence.
2. Endpoint and network indicators are being correlated to establish scope.
Use this during a technical investigation involving multiple data sources.
Meaning: Analysts are connecting evidence across systems to understand the incident.
3. Potentially affected assets are being identified and prioritized.
Use this when responders are determining which systems may require attention.
Meaning: The team is mapping the possible impact.
4. Relevant authentication activity is being reviewed for anomalies.
Use this when unusual account behavior may be involved.
Meaning: Login and access activity is being examined for suspicious patterns.
5. Security logs are being preserved for investigative analysis.
Use this when evidence preservation is important.
Meaning: Relevant records are being retained for investigation.
6. Indicators associated with the incident are being tracked across the environment.
Use this when responders are searching for related activity.
Meaning: Known signs of the incident are being checked across systems.
7. Affected systems are being isolated where appropriate.
Use this when containment requires restricting potentially compromised systems.
Meaning: Isolation is being considered or applied to reduce further risk.
8. Access activity is being reviewed to determine whether unauthorized use occurred.
Use this when an account or authentication event is suspicious.
Meaning: The team is checking whether access was legitimate.
9. The incident timeline is being reconstructed from available evidence.
Use this when investigators need to establish the sequence of events.
Meaning: Technical records are being used to understand what happened and when.
Calm And Reassuring Responses
1. The situation is being actively monitored and managed.
Use this when stakeholders need reassurance without unnecessary detail.
Meaning: Appropriate personnel are actively handling the event.
2. We are taking measured steps to understand and contain the issue.
Use this when avoiding panic during an early investigation.
Meaning: The response is deliberate rather than rushed.
3. The team is following the established incident response process.
Use this when coworkers ask whether there is a plan.
Meaning: The situation is being handled according to predefined procedures.
4. We are focusing on verified information and avoiding assumptions.
Use this when rumors are spreading internally.
Meaning: Communication will be based on confirmed evidence.
5. The investigation is progressing, and we will share verified updates.
Use this when people are waiting for more information.
Meaning: Further communication will come as reliable findings emerge.
6. Appropriate containment measures are being considered.
Use this when the team is evaluating how to limit potential impact.
Meaning: The response team is actively considering risk-reduction actions.
7. We understand the concern and are treating the incident seriously.
Use this when employees or customers are worried.
Meaning: Their concern is acknowledged without exaggerating the situation.
8. Our priority is to protect systems while maintaining essential operations.
Use this when explaining the balance between security and business continuity.
Meaning: Security and operational stability are both being considered.
Executive Responses
1. We are currently managing a cybersecurity incident and assessing its business impact.
Use this for a concise leadership update.
Meaning: Executives are being informed about both the incident and its potential organizational effect.
2. The response team is assessing scope, impact, and containment requirements.
Use this in executive-level reporting.
Meaning: Leadership is being updated on the major decision areas.
3. Current findings are preliminary and remain under investigation.
Use this when leadership requests an early assessment.
Meaning: The available information may change as evidence is reviewed.
4. Business-critical systems are being prioritized during the response.
Use this when operational continuity is a major concern.
Meaning: Resources are being focused on important services.
5. Relevant response teams are coordinating actions and communications.
Use this when several departments or specialists are involved.
Meaning: The response is being managed across organizational functions.
6. We are maintaining an evidence-based incident timeline.
Use this when leadership needs a reliable account of events.
Meaning: Documented evidence is being used to establish what happened.
7. Recovery decisions will follow containment and validation activities.
Use this when discussing restoration.
Meaning: Systems will not simply be returned to normal without appropriate checks.
8. The incident response plan is guiding current actions.
Use this when leadership asks how the organization is responding.
Meaning: Existing procedures are being used to coordinate the response.
9. We are evaluating operational, security, and communication considerations in parallel.
Use this when the incident affects multiple areas.
Meaning: Response decisions consider more than technical remediation.
Customer-Friendly Responses
1. We are investigating a security issue affecting our environment.
Use this when customers need a simple initial notification.
Meaning: A security concern exists and is being investigated.
2. Our security team is actively reviewing the situation.
Use this when communicating with customers before detailed findings are available.
Meaning: The organization is actively responding.
3. We are taking appropriate steps to protect our systems and services.
Use this when reassuring customers about ongoing security actions.
Meaning: Protective measures are being taken.
4. We are working to determine the scope and impact of the incident.
Use this when the investigation is still developing.
Meaning: The organization is establishing what may have been affected.
5. We will communicate verified information as it becomes available.
Use this when customers want immediate details.
Meaning: Updates will be based on confirmed findings.
6. We understand that security concerns can be disruptive and frustrating.
Use this when acknowledging customer concerns.
Meaning: The organization recognizes the customer experience during an incident.
7. Our response process includes investigation, containment, and recovery.
Use this when explaining the overall approach.
Meaning: The organization has a structured method for handling the incident.
8. We are coordinating with the appropriate security and operational teams.
Use this when explaining who is handling the issue.
Meaning: Relevant specialists are working together.
9. We are monitoring our services for additional signs of suspicious activity.
Use this when ongoing monitoring is part of the response.
Meaning: The organization is watching for related activity.
Short And Direct Responses
1. Incident confirmed. Response activated.
Use this for a concise internal status message.
Meaning: The event has been confirmed and formal response is underway.
2. Investigation is in progress.
Use this when details are still being established.
Meaning: Responders are actively examining the incident.
3. Containment is underway.
Use this when immediate risk-reduction actions have started.
Meaning: The team is working to limit the incident.
4. Scope is still being assessed.
Use this when the full impact is unknown.
Meaning: Investigators are determining how far the incident extends.
5. Relevant teams have been notified.
Use this after required stakeholders receive an alert.
Meaning: Communication procedures have been initiated.
6. Systems remain under monitoring.
Use this during active observation.
Meaning: Responders are watching systems for additional activity.
7. Evidence is being preserved.
Use this when investigation records are being secured.
Meaning: Relevant information is being retained for analysis.
8. Recovery planning has started.
Use this after containment activities begin progressing.
Meaning: The team is preparing for restoration.
9. Updates will follow verified findings.
Use this when information is incomplete.
Meaning: Future updates will prioritize accuracy.
Email And Workplace Responses
1. Subject: Cybersecurity Incident Update
Use this as an email subject when distributing a formal security update.
Meaning: The email contains information about an active or recent incident.
2. Please be aware that a potential security incident is currently under investigation.
Use this when notifying employees through email.
Meaning: Employees should know that an investigation is taking place.
3. The security team is currently assessing the situation.
Use this in an internal status email.
Meaning: Security specialists are evaluating the event.
4. Please avoid sharing unverified information about the incident.
Use this when rumors are circulating at work.
Meaning: Employees should rely on confirmed information.
5. We will provide further instructions if any employee action is required.
Use this when employees may eventually need to respond.
Meaning: Staff will receive clear directions if needed.
6. Please direct security-related questions through the designated response channel.
Use this when centralizing communication.
Meaning: Incident questions should go through the appropriate team.
7. The incident remains under active investigation.
Use this in recurring workplace updates.
Meaning: The situation has not yet been fully resolved.
8. Current findings should be considered preliminary.
Use this when sharing early investigation results.
Meaning: Initial findings may change.
9. Business operations are being monitored alongside the security response.
Use this when the incident has operational implications.
Meaning: Security and business continuity are being handled together.
Incident Report Responses
1. The incident was detected through security monitoring activity.
Use this when documenting how the event was initially identified.
Meaning: Monitoring controls played a role in detection.
2. Initial investigation began after suspicious activity was identified.
Use this when recording the start of the investigation.
Meaning: Unusual behavior triggered further analysis.
3. The response team assessed the available evidence and affected assets.
Use this in a formal incident report.
Meaning: Responders reviewed technical information and potentially affected systems.
4. Containment measures were implemented based on the available findings.
Use this when documenting response actions.
Meaning: Steps were taken to limit potential impact.
5. Relevant logs and evidence were preserved for further analysis.
Use this when documenting investigative procedures.
Meaning: Evidence was retained for review.
6. The incident timeline was developed using available technical records.
Use this when writing the investigation summary.
Meaning: Records were used to reconstruct events.
7. The potential impact was assessed as part of the investigation.
Use this when documenting impact analysis.
Meaning: Investigators evaluated possible consequences.
8. Recovery activities followed completion of containment requirements.
Use this when describing restoration.
Meaning: Recovery began after appropriate containment steps.
9. Systems were validated before returning to normal operation.
Use this when documenting recovery controls.
Meaning: Systems were checked before full restoration.
Confident Responses
1. We have a plan, and we are following it.
Use this when reassuring a team during an active incident.
Meaning: The response is organized around established procedures.
2. We are focusing on facts, not assumptions.
Use this when people are making premature conclusions.
Meaning: Decisions are being based on verified evidence.
3. The response team is already working through the next steps.
Use this when stakeholders need reassurance about progress.
Meaning: Appropriate actions are already underway.
4. We are addressing the issue systematically.
Use this when describing a structured response.
Meaning: The team is handling the incident in an organized way.
5. Every response action is being tracked.
Use this when emphasizing accountability.
Meaning: Actions and decisions are being documented.
6. We are keeping containment and recovery moving together.
Use this when operations and security teams are coordinating.
Meaning: The response is addressing both immediate risk and restoration.
7. We are not rushing conclusions before the evidence is ready.
Use this when someone demands an immediate explanation.
Meaning: Accuracy is being prioritized over speculation.
8. The right teams are involved.
Use this when stakeholders ask who is handling the incident.
Meaning: Relevant expertise has been brought into the response.
9. We are keeping communication clear and consistent.
Use this during a fast-moving incident.
Meaning: The organization is trying to prevent conflicting messages.
Clever Responses
1. Detect first, assume later.
Use this as a memorable internal reminder during an investigation.
Meaning: Evidence should come before conclusions.
2. Every alert deserves context.
Use this when discussing security alerts with a team.
Meaning: Alerts should be investigated rather than interpreted in isolation.
3. Good incident response starts with good questions.
Use this during investigation planning.
Meaning: Asking the right questions helps establish what actually happened.
4. Logs tell the story, but context fills in the blanks.
Use this when discussing technical investigation.
Meaning: Raw data becomes more useful when combined with surrounding information.
5. Containment buys time, investigation builds understanding.
Use this when explaining response priorities.
Meaning: Limiting impact and learning what happened are connected but distinct goals.
6. A fast response still needs a clear head.
Use this during a stressful security event.
Meaning: Speed should not eliminate careful decision-making.
7. The incident ends when the lessons begin.
Use this after recovery activities.
Meaning: Post-incident learning is an important part of response management.
8. Every response action should answer a question.
Use this when encouraging deliberate investigation.
Meaning: Actions should have a clear investigative or protective purpose.
9. Visibility turns suspicious activity into useful evidence.
Use this when discussing monitoring and logging.
Meaning: Good visibility helps investigators understand unusual behavior.
Urgent Responses
1. Immediate attention is required.
Use this when a security event needs prompt action.
Meaning: The issue should be addressed without unnecessary delay.
2. Please escalate this incident through the established response channel.
Use this when an alert requires formal escalation.
Meaning: The event should reach the appropriate responders.
3. Potentially affected systems require immediate assessment.
Use this when suspicious activity may involve important assets.
Meaning: The relevant systems should be reviewed promptly.
4. We are initiating containment procedures.
Use this when immediate risk reduction has begun.
Meaning: The response team is taking steps to limit potential impact.
5. Please preserve relevant evidence and avoid unnecessary system changes.
Use this during an investigation where evidence may be important.
Meaning: Teams should avoid actions that could interfere with investigation.
6. The incident response team has been notified.
Use this after escalation.
Meaning: Appropriate security personnel are now aware of the event.
7. We are prioritizing the affected environment for investigation.
Use this when resources need to be focused quickly.
Meaning: The suspected affected area is receiving immediate attention.
8. Additional suspicious activity is being assessed.
Use this when related indicators may exist.
Meaning: Responders are checking whether the incident extends further.
9. Please follow all temporary security instructions until further notice.
Use this when employees need to follow temporary controls.
Meaning: Staff should comply with current response requirements.
Post-Incident Responses
1. The incident response phase has concluded, and post-incident review is underway.
Use this after immediate response activities are complete.
Meaning: The organization has moved from active response to analysis.
2. We are reviewing what happened and how the response performed.
Use this during a lessons-learned review.
Meaning: Both the event and response process are being evaluated.
3. Corrective actions have been identified for follow-up.
Use this when improvements have been documented.
Meaning: The organization has identified changes to address discovered issues.
4. Preventive measures are being considered based on the findings.
Use this after identifying opportunities to reduce future risk.
Meaning: The organization is exploring ways to prevent similar events.
5. The incident timeline has been finalized using available evidence.
Use this after completing investigation documentation.
Meaning: The sequence of events has been formally recorded.
6. Response documentation has been completed for future reference.
Use this when closing incident records.
Meaning: Important information has been preserved.
7. Relevant teams are reviewing the lessons learned.
Use this when multiple departments participated in the response.
Meaning: Teams are sharing findings to improve future readiness.
8. Security controls will be reviewed where appropriate.
Use this when the incident revealed potential control gaps.
Meaning: Existing protections may be reassessed.
9. The response process will be updated where improvements are identified.
Use this when incident findings suggest process changes.
Meaning: Procedures may be refined based on experience.
FAQs
What Is A Simple Response To A Cyber Incident?
A simple response can be: “We have identified a potential security incident and are actively investigating it.” It communicates awareness without making unsupported claims.
What Should You Say During A Cybersecurity Incident?
Keep the message factual, concise, and action-oriented. Mention what is confirmed, what is being investigated, what actions are underway, and where people should look for official updates.
What If You Do Not Know The Full Impact Yet?
Say that the impact is still being assessed. Avoid guessing about affected systems, data, users, or causes until the investigation provides enough evidence.
Can Cyber Incident Response Management Be Used In A Workplace?
Yes. It can cover internal security alerts, suspicious account activity, malware incidents, unauthorized access, data security events, system disruptions, and other cybersecurity situations.
Is Humor Appropriate During A Cybersecurity Incident?
Humor can work in informal internal communication when the situation allows it, but serious incidents involving customers, sensitive information, or major operational impact generally require clear and professional communication.
What Should You Avoid Saying During An Incident?
Avoid speculation, exaggerated claims, blame, unverified details, unsupported assurances, and statements that promise outcomes before the investigation confirms them.
How Should You Communicate With Customers?
Use simple language, acknowledge the situation, explain that the investigation is ongoing, provide verified information, and tell customers whether they need to take any action.
Conclusion
Cyber incident response management is about more than reacting when something goes wrong. It is about having the right process, communicating clearly, and helping everyone understand what happens next. Whether you need a quick internal update, a professional customer message, an executive status report, or a post-incident statement, the right wording can make a stressful situation easier to manage.
Do not be afraid to adapt these responses to match your organization, audience, and incident stage. Keep messages factual, concise, and easy to understand. Save this list for the next security alert, share it with your team, and reuse the responses that fit your workflow. Clear communication can be one of the most useful parts of a well-managed incident response.